
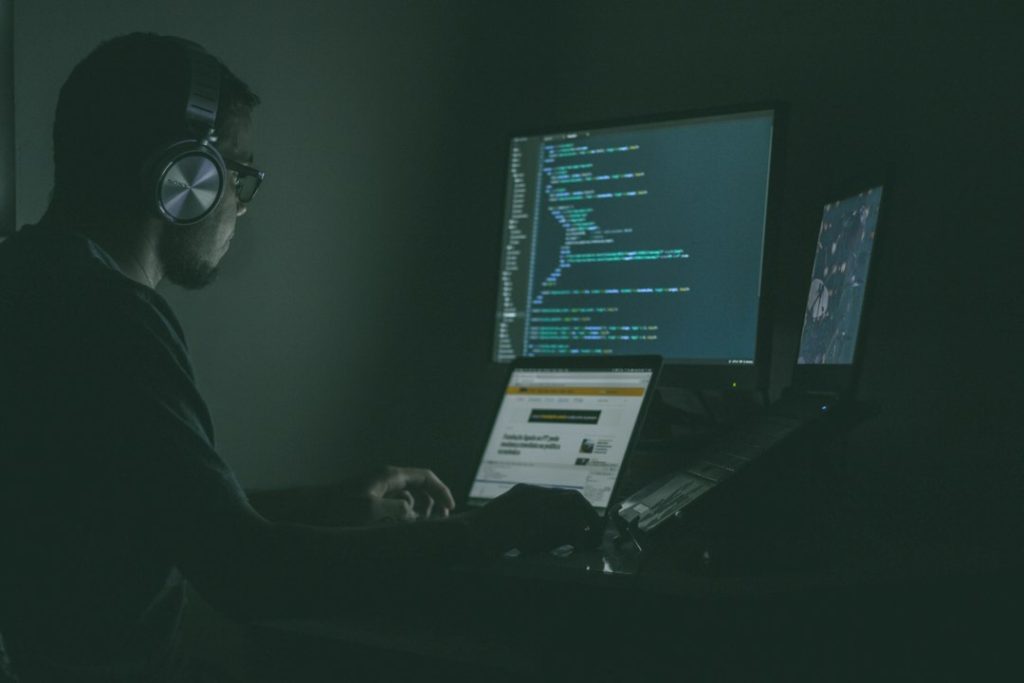
Programmer reviewing code on a laptop illustrating smart contract security auditing
A Smart Contract Was Audited. Here Are Seven Reasons That Does Not Make It Safe
“Audited” is one of the most reassuring words in decentralized finance—and one of the easiest to misunderstand. An independent review can identify real problems, but it only examines the code and assumptions within its scope at a particular time. The deployed system can later change; a privileged administrator can override rules; or the vulnerability may sit in a dependency the audit did not cover.
Ethereum’s smart-contract security guidance warns that audits are not a silver bullet. OpenZeppelin’s access-control documentation explains how ownership and roles may govern minting, pausing, upgrades and transfers. These are useful foundations for a reader who wants to assess a protocol without pretending to perform a full code audit.
The goal of this guide is to show exactly what an audit badge cannot guarantee, and to give readers a practical process for finding the remaining risks before approving a transaction or depositing collateral.
Latest Stories
Europe Is Testing Tokenized Collateral for Clearing — The Default Scenario Is the Real Test
Thailand’s Bitcoin and Ether ETF Rules Start October 16 — But Approval Isn’t Automatic
Staking APY Is Not Your Real Return: A Practical Guide to Fees, Slashing and Liquidity
Seven gaps between an audit report and live security
- The audited version might not be deployed. Locate the exact commit hash, contract address, source-code repository and network named in the report. A newer implementation or a contract on a different chain could contain changes the auditor never reviewed.
- Audit scope may exclude crucial components. Ask whether vaults, oracles, off-chain signers, bridges, pricing logic, governance contracts and external libraries were included. “Core contracts reviewed” is not identical to end-to-end security of the product.
- Findings may remain unresolved. Read the severity table and remediation status. Some teams accept risks or postpone fixes. A polished PDF should not distract from a critical issue explicitly listed as acknowledged or unresolved.
- Upgradeable proxies can change behavior. A proxy can preserve the same public address while routing calls to new code. The OpenZeppelin upgrade guide explains that implementation logic can be replaced. Check the current implementation address, authority that controls it and any upgrade delay.
- Admin keys can override user expectations. Owners may be able to pause withdrawals, change risk parameters, whitelist wallets, mint tokens or update oracles. A multisig raises the cost of a single-key compromise, but users still need to know who the signers are and whether their actions are time-locked.
- External dependencies can fail independently. Even carefully reviewed contracts can suffer when an oracle reports a bad price, a bridge is compromised, or a third-party protocol changes collateral rules. Dependency risk grows with the number of linked contracts and chains.
- Security degrades without monitoring. Markets, attack techniques and operational assumptions evolve. A protocol should publish incident procedures, change logs, bug-bounty rules and current notices. An old audit may offer little insight into a system modified dozens of times afterward.
Illustrative example: a vault audited in January holds stablecoins and relies on an external price oracle. In March, the team upgrades the vault implementation and gives a new signer emergency administrative access. The January report may still be genuine, but it is not enough to establish whether the March system handles oracle failure or signer compromise safely. This example is hypothetical; it does not describe a specific project.
Some claims require technical confirmation. Source-code verification checks whether published source corresponds to deployed bytecode. It is not the same as formal verification that code fulfills a security specification. Users should not confuse a block explorer’s green “verified” label with a comprehensive security review.
A practical five-minute review for non-developers
Find the protocol’s official documentation and contract addresses. Follow those addresses to a recognized block explorer and check whether source code is verified. Locate the implementation and proxy status, then identify the governance or owner address if exposed. If the interface hides these basics, mark the information gap rather than assuming a good reason.
Next, open the audit PDF. Look for the audit date, exact code commit, reviewed contracts, out-of-scope sections and findings table. Check whether the claimed fix was actually retested and whether any release occurred after the engagement. An independent assessment is strongest when it can be tied to deployed code and a documented remediation trail.
Finally, consider what happens if the system must stop. Can the team pause deposits without freezing exits? Is an emergency withdrawal mechanism documented? Does the protocol explain oracle incidents, compromised admin keys or failed upgrades? A secure operational posture includes honest communication about failure scenarios.
Our wallet permission guide covers one user-level risk that also survives code reviews: unlimited token approvals can remain active even after disconnecting a website.
Bottom line: a real audit is positive evidence of review, not proof of immunity. Verify code identity, scope, remediation, privileged access, dependencies and response procedures. Treat any missing answer as a reason for more investigation before risking assets.
Sources and method: Ethereum Foundation contract-security and verification guidance plus OpenZeppelin access-control and upgrade documentation, reviewed October 12, 2026.
How do you rate this article?
Subscribe to our YouTube channel for crypto market insights and educational videos.

Join our Socials
Briefly, clearly and without noise – get the most important crypto news and market insights first.
8
Also read
Similar stories you might like.
Blockchain
Europe Is Testing Tokenized Collateral for Clearing — The Default Scenario Is the Real Test
TechGaged | 2026-10-12
Bitcoin
Thailand’s Bitcoin and Ether ETF Rules Start October 16 — But Approval Isn’t Automatic
TechGaged | 2026-10-12
Blockchain
Staking APY Is Not Your Real Return: A Practical Guide to Fees, Slashing and Liquidity
TechGaged | 2026-10-12
Crypto News
SEC Crypto Custody Proposal Opens a Conditional Self-Custody Path for Regulated Funds
TechGaged | 2026-10-12
Bitcoin
Bitcoin ETF Premiums and Discounts: The Cost Investors Miss When Comparing Fees
TechGaged | 2026-10-12
Crypto News
CFTC Draws a New Line Between Prediction Market Event Contracts and Casino Wagers
TechGaged | 2026-10-12
Crypto Guides
Proof of Reserves Is Not Proof of Solvency: Eight Tests for a Crypto Exchange
TechGaged | 2026-10-12
Crypto News
EU Crypto Platforms Face New ESMA Stablecoin Restrictions — Even Custody Is in Scope
TechGaged | 2026-10-12
Blockchain
How Safe Is an Ethereum Layer 2? Five Risks That TVL and Transaction Speed Cannot Show
TechGaged | 2026-10-12
Blockchain
Which Blockchains Generate Real Revenue? Fees, Token Incentives and the Numbers That Matter
TechGaged | 2026-10-10