
Polygon AI agent stablecoin spending limits editorial illustration
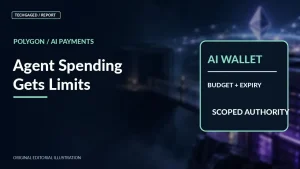
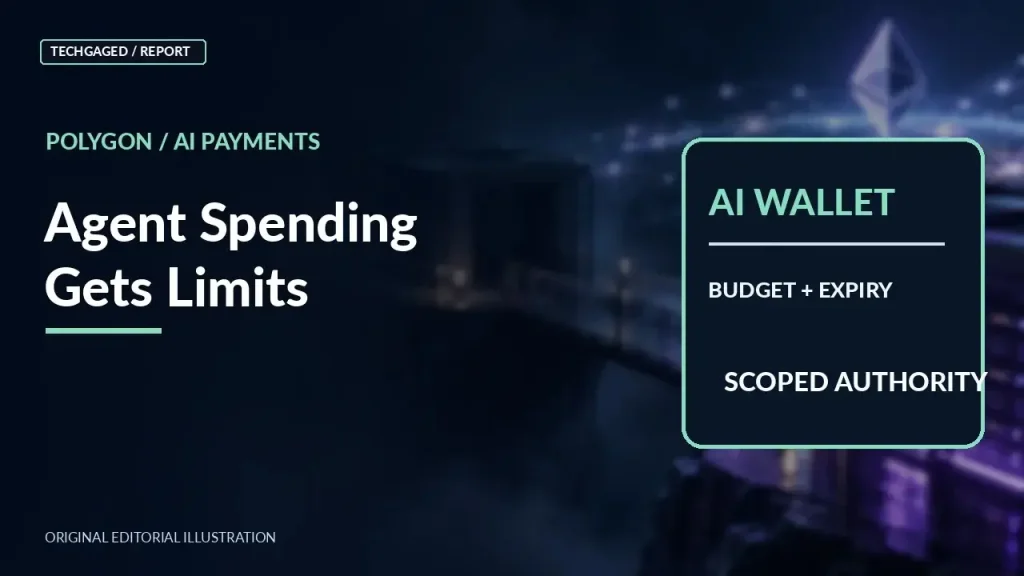
Polygon has introduced spending controls for AI agents using stablecoin payments, addressing one of the main security obstacles to machine-initiated commerce: how to authorize software to complete a narrow financial job without giving it unlimited access to a wallet.
The October 21 product announcement says Polygon Open Money Stack can enforce an agent’s defined payment budget, permitted actions and expiration time against an existing wallet. The model is aimed at tasks such as buying approved API credits or computing services when usage crosses a threshold.
The important part is delegation. An agent can be instructed to perform a task, but its textual instructions should not by themselves define how much it can transfer. The wallet or payment service needs controls that remain effective even if the software is tricked into making a different decision.
Latest Stories
Unichain Moves Toward OP Enterprise With Native Cross-Rollup Transfers Planned
Chainlink’s Vault Adapters Open One DeFi Vault to Deposits From 80+ Chains
Polygon Automates Stablecoin Payouts With Recipient and Budget Controls
Scoped permission is safer than open-ended authority
Consider an AI system that needs to purchase data from a service provider. Requiring a fresh human signature for every tiny request may make automated workflows impractical. Granting a permanent unrestricted wallet permission, however, creates a severe loss scenario if the agent or its environment is compromised.
Polygon’s approach lets an organization set specific conditions: a maximum budget, approved types of activity and a window during which the permission is valid. Each attempted transfer can then be tested against those constraints before completion.
These safeguards do not mean an agent can reliably distinguish every legitimate seller from an attacker. An approved destination could itself be compromised, and an attacker might attempt many small transactions that remain within the limit. Monitoring and anomaly detection still matter.
How businesses should adopt agent payments
Financial teams should use the least privilege necessary, short expiration periods, limits per supplier and explicit policies for revocation. Sensitive payments may require additional approval, especially if the agent can change counterparties or move large balances.
They also need records that attribute each transfer to an agent, business purpose and supervising human. An automated authorization policy does not eliminate accountability for compliance, sanctions screening or unauthorized disbursements.
System design must consider prompt-injection attacks: content from a webpage, document or tool response could try to redirect an agent toward an unintended payment. Guardrails should therefore be enforced outside the language model itself, by the transaction approval service.
The announcement is a useful example of narrowing the risk of agentic finance with practical constraints. Its success will depend on whether the controls hold under adversarial conditions and whether organizations deploy them conservatively rather than treating autonomous payments as automatically safe.
How do you rate this article?
Subscribe to our YouTube channel for crypto market insights and educational videos.

Join our Socials
Briefly, clearly and without noise – get the most important crypto news and market insights first.
Most Read Today
1
Ripple Wins Final US Trust Bank Approval, but RLUSD Issuer Remains Unchanged
2S&P Global Ratings Brings DeFi Vault Risk Assessments Onchain Through Chainlink
3Hanwha Selects Chainlink for Global Tokenized Assets Ahead of Korea’s 2027 Rules
4Circle Opens CCTP to More Than USDC: A New Route for Issuer-Controlled Tokens
5EU Crypto Firms Face Deadline to Unwind Non-MiCA Stablecoin Exposure
Latest
8
Also read
Similar stories you might like.
Industry
Polygon Automates Stablecoin Payouts With Recipient and Budget Controls
TechGaged | 2026-11-02
Industry
Coinbase Rebuilds Account Permissions for Businesses Without Replacing Its Retail Core
TechGaged | 2026-11-02
Defi
Euro-to-Dollar Stablecoin Swaps Go Live on Polygon Through Monerium and Frax
TechGaged | 2026-11-02
Industry
Polygon Opens TRON USDT Routing to Banks and Fiat Payout Networks
TechGaged | 2026-11-02
Blockchain
Polygon CDK Besu Connects Private Bank Chains to Public Liquidity With ZK Proofs
TechGaged | 2026-11-02
Industry
Polygon Open Money Stack Adds Solana for Full Bank-to-Stablecoin Payments
TechGaged | 2026-11-02
Crypto News
AI Agent Crypto Weakens — The Next Sell-Off Could Depend on This Signal
Azeez | 2026-10-26
Crypto News
Zcash’s Next Security Milestone Could Fuel Bullish Hopes for ZEC
Azeez | 2026-10-13
Crypto News
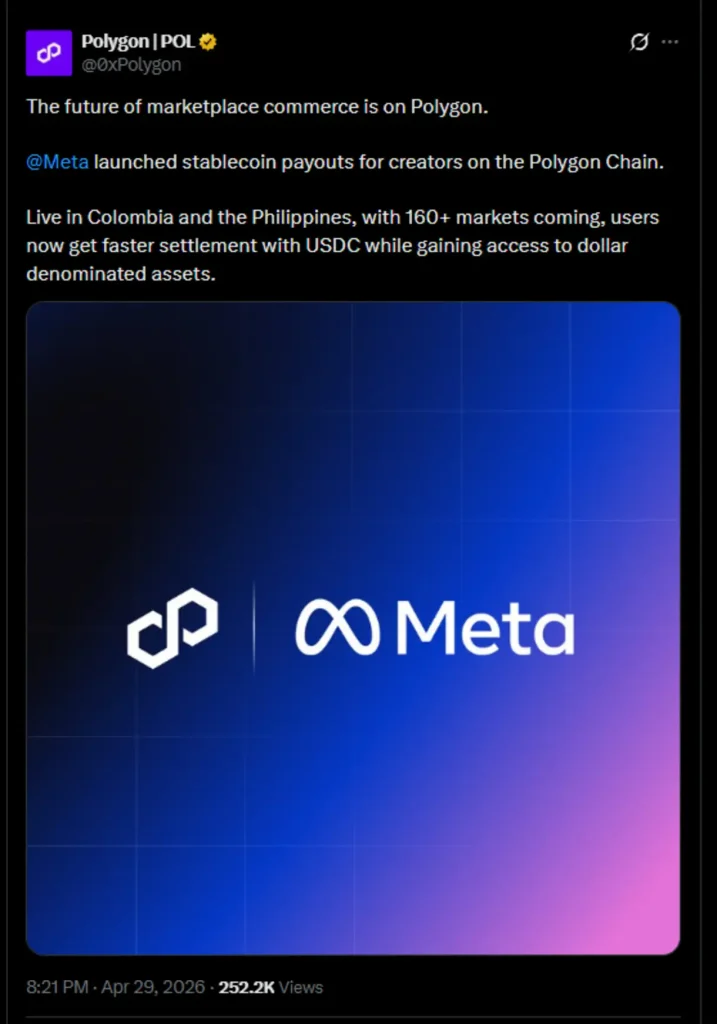
Polygon Updates POL’s MiCA White Paper as EU Trading Access Expands
TechGaged | 2026-10-04
Blockchain
Polygon Ships Bor v2.10.2 With Faster State-Root Processing and New Witness Messaging
TechGaged | 2026-10-04